Microsoft Security | Microsoft Entra | Microsoft Entra ID
A cloud-based identity and access management service for securing user authentication and resource access

This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EJW%3C/text%3E%3C/svg%3E)
We have a AD Conditional Access policy enabled to block all international traffic to azure and O365 resources. How I can make exceptions for specific users traveling to specific countries.
A cloud-based identity and access management service for securing user authentication and resource access
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMT%3C/text%3E%3C/svg%3E)
Hi @Jesse Wrenn ,
Just following up to see if you were able to get the information you need. Another option would be to simply configure the Conditional Access policy to require MFA instead of blocking the accounts.
If you were able to get the answer resolved it would help me if you could mark the answer to improve searchability, but otherwise let me know if you have further questions!
Hi @Jesse Wrenn ,
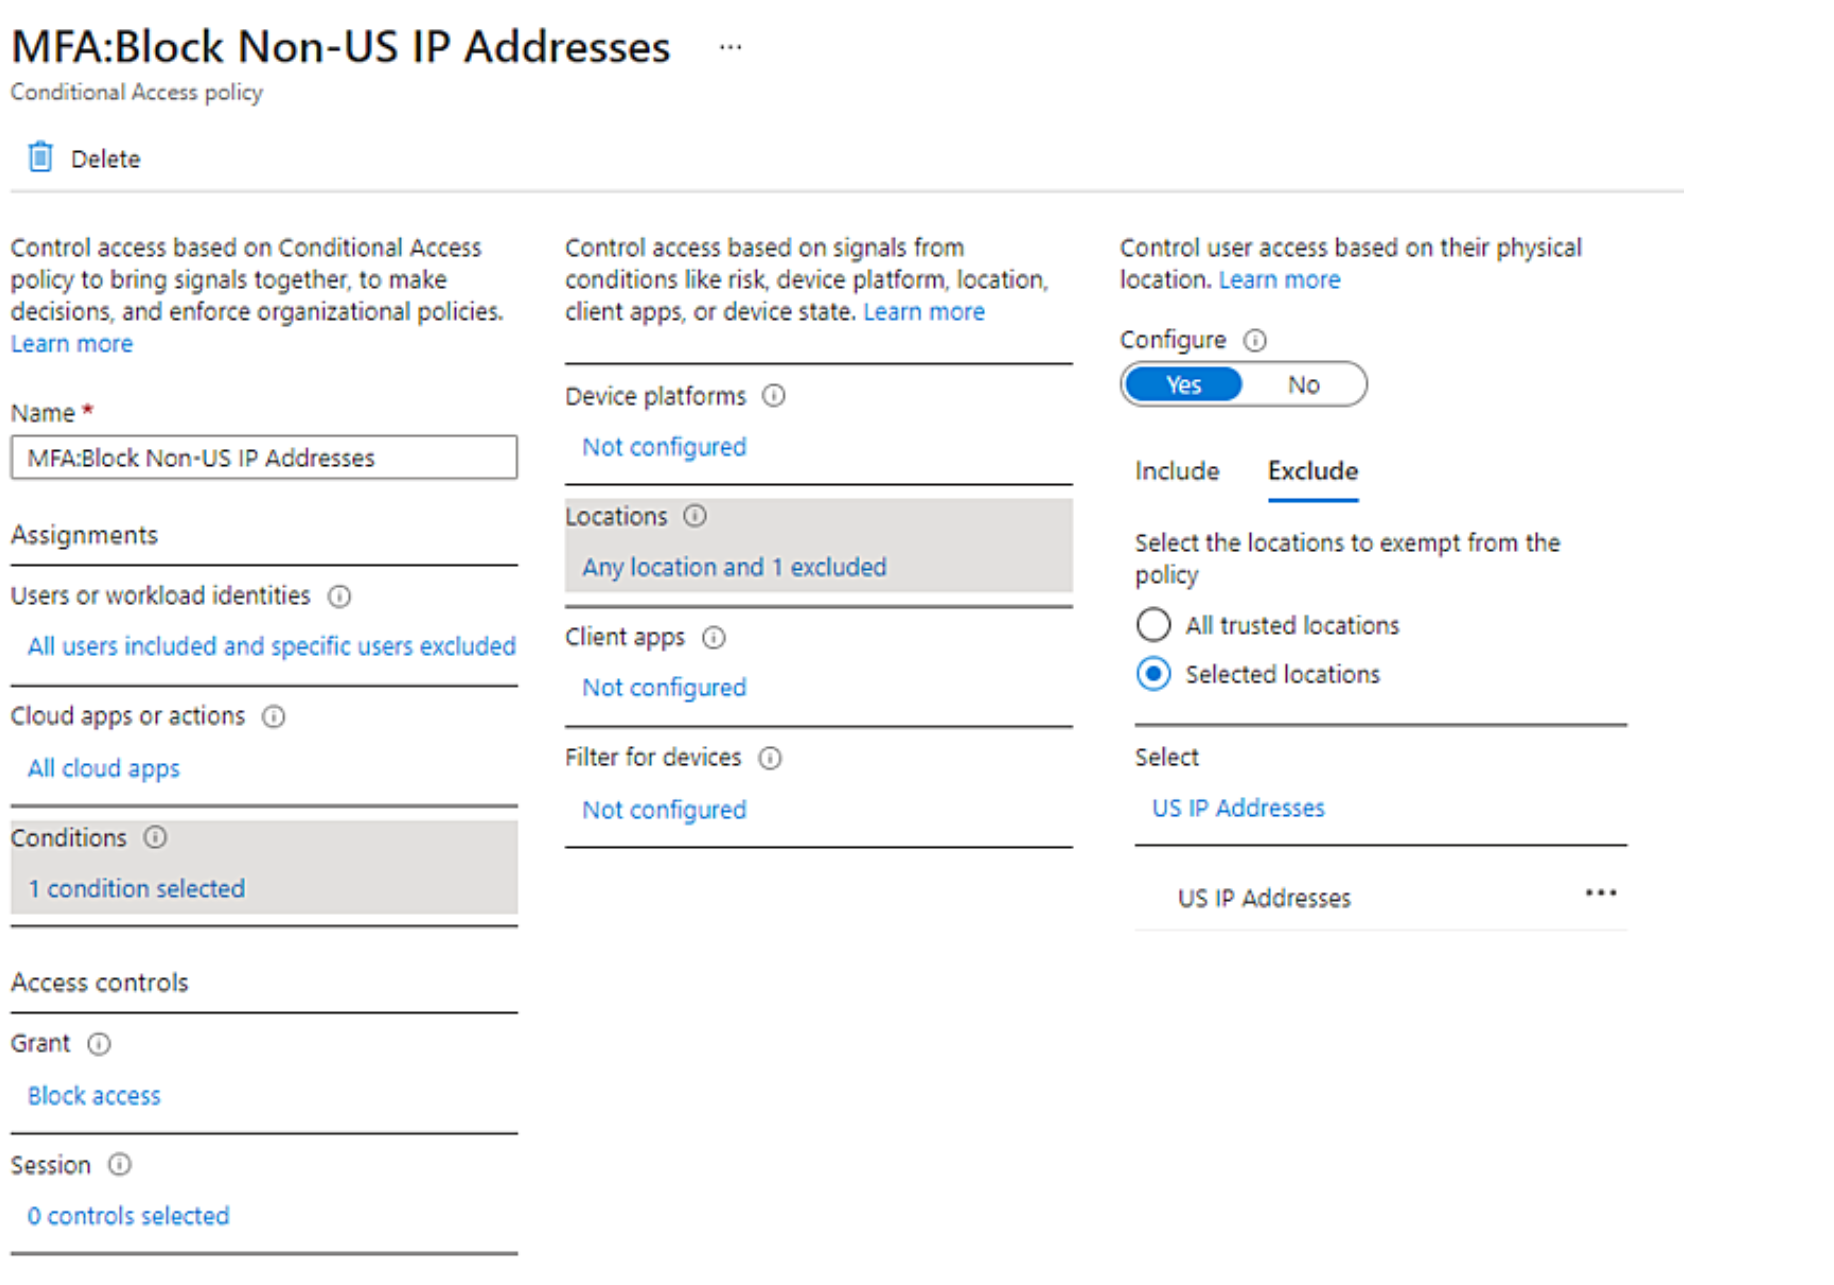
A good way to grant access to specific users traveling to specific countries is to create a universal "exclude" group in your Conditional Access policies, and then add those users to that group when they are traveling.
Then if you enforce MFA for untrusted locations and have those users added as an exemption to your "block international countries", any attempts to access those accounts outside of your trusted locations will still be prompted for MFA.
So in summary, you can have a general policy to block access from "All locations" or all international locations, and then exclude the countries where you want to allow access. You would then create a separate policy to enforce MFA for all locations and exclude the ones marked as "trusted." When your users go on vacation, you can add them to your "universal exclude" group and remove them from that group when they return.
There isn't a way to add a specific policy around a specific user and country, but the above solution should achieve basically the same goal.
There is a similar discussion around this topic in Spiceworks where several users have added their solutions, including this sample policy:
I have left feedback for the product team to include more granular controls for these types of scenarios, but if you also want to leave feedback for them and include your specific use case you can add that in User Voice or share it with me to pass along. https://feedback.azure.com/
I hope this helps!
-
If the information helped you, please Mark the answer. This will help us and other community members as well.