Azure VPN Gateway
An Azure service that enables the connection of on-premises networks to Azure through site-to-site virtual private networks.
This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EBP%3C/text%3E%3C/svg%3E)
Hello,
I'm having trouble understanding the notion related to the "use remote gateways" option.
I want to peer multiple spoke vnets to a hub that has a Virtual Network Gateway for S2S tunnel to on-premise infrastructure. I want that communication works in both way (Azure to on-prem and on-prem to Azure).
Is the option "use remote gateways" intended to allow communication from peered network to on-premise through the S2S tunnel? If yes, I have noticed in documentation that using this option is allowed only for one peered network. Am I understanding well?
If yes, what is the alternative then?
Thanks a lot for the clarification.
Best regards.
An Azure service that enables the connection of on-premises networks to Azure through site-to-site virtual private networks.
An Azure networking service that is used to provision private networks and optionally to connect to on-premises datacenters.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EMS%3C/text%3E%3C/svg%3E)
Does "enable vnet to use vet's remote gatway" also control RDP access to all servers on that vnet?

No, this setting just allows access to Virtual Network Gateways on the remote network, used for VPN connections. Peered VNETs will have access to RDP to any VMs on the connected networks but you can restrict this with deny rules in the Network Security Groups.
Thank you and I appreciate the quick reply/answer.
@Alan Kinane
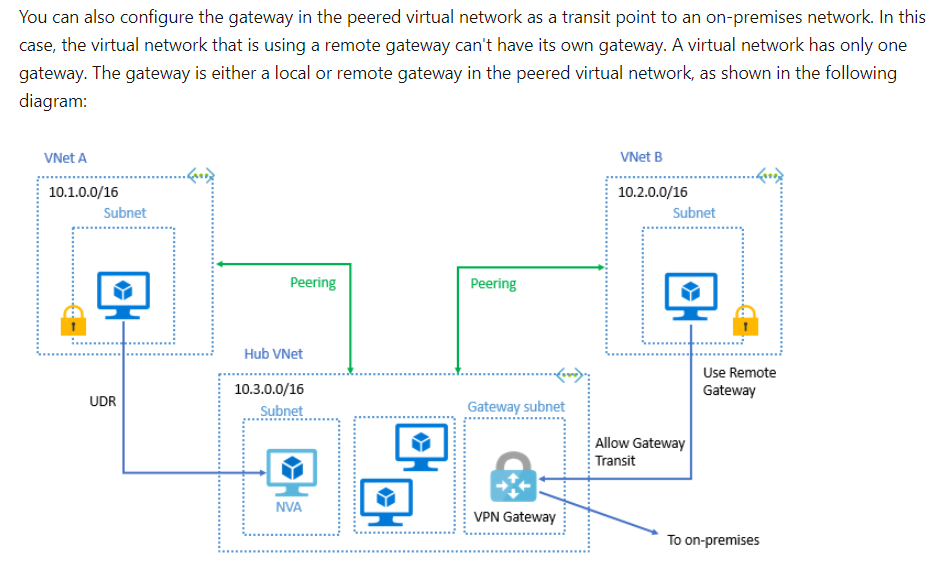
Thank you for your reply. Is that implied that all spoke vnets can communicate with on-premise or not ? What is the goal of NVA appliance in the diagram above?
Yes, all spoke VNETs can use the remote gateway in the hub VNET. The NVA is a Network Virtual Appliance, essentially a firewall. Not necessarily a requirement, it was just present in this example.
Yes, it is as you described. You can have your VNETs transit through the VPN gateway and access your on-premises networks. You can have multiple peered VNETs but the limitation is that you can only have one VPN gateway, i.e. you can't peer VNETs that each have a VPN gateway.