Azure Kubernetes Service
An Azure service that provides serverless Kubernetes, an integrated continuous integration and continuous delivery experience, and enterprise-grade security and governance.
This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EUK%3C/text%3E%3C/svg%3E)
Let's say I created a new aks cluster(newcluster) and kept in a resource group(newrg).
Then, another resource group also getting created with name MC_newrg_newcluster_eastus.
It contains below resources.

Why it is created and the purpose of it?
Because of this, cluster can't be deleted directly.
We need to delete this rg first and then able to delete cluster.
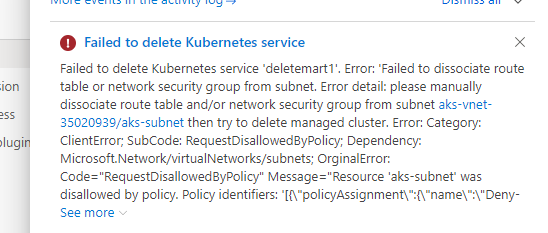
Else, getting this error.
Similar to this.
An Azure service that provides serverless Kubernetes, an integrated continuous integration and continuous delivery experience, and enterprise-grade security and governance.

AKS creates this other resource group so that it can automatically create
As stated from the AKS FAQ section about this extra resource group:
The second resource group, known as the node resource group, contains all of the infrastructure resources associated with the cluster. These resources include the Kubernetes node VMs, virtual networking, and storage. By default, the node resource group has a name like MC_myResourceGroup_myAKSCluster_eastus. AKS automatically deletes the node resource group whenever the cluster is deleted, so it should only be used for resources that share the cluster's lifecycle.
You can change the Resource Group name if you want, but AKS manages the resource group (and all resources within it). This allows AKS to create VMs, clusters, instances ect... for you. When you delete the AKS cluster, AKS SHOULD delete this resource group for you.
In the error you listed, a NSG was added to the subnet that has a policy that AKS does not have permission to delete. This is why you had to delete that resource group manually. If you do not want to do this in the future, you can remove any policies on NSGs for AKS resource groups. Many orgs put these NSGs & policies on automatically.